Program Details
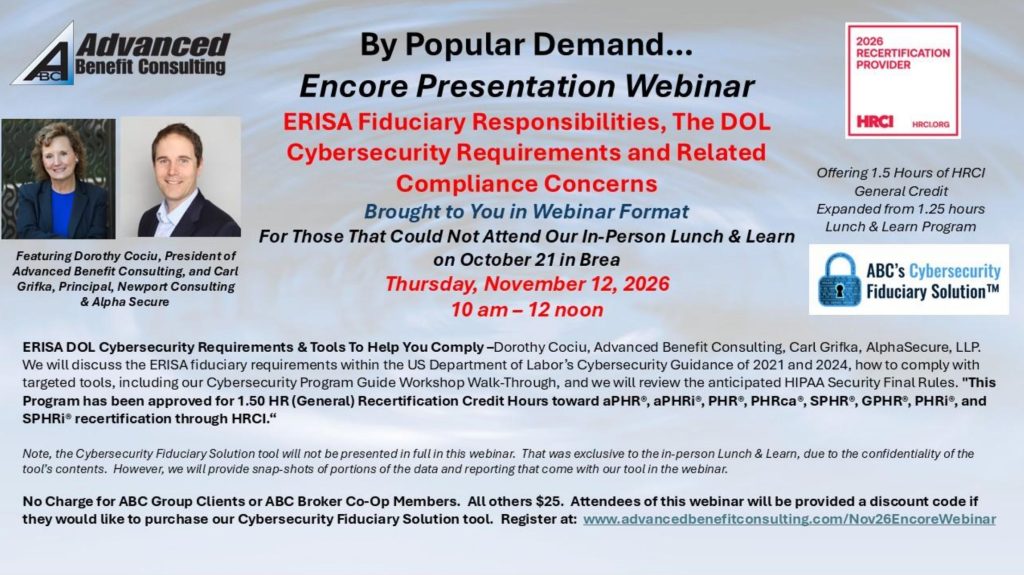
ERISA DOL Cybersecurity Requirements & Tools To Help You Comply –Dorothy Cociu, Advanced Benefit Consulting, Carl Grifka, AlphaSecure, LLP. We will discuss the ERISA fiduciary requirements within the US Department of Labor’s Cybersecurity Guidance, how to comply with targeted tools, including our Cybersecurity Program Guide Workshop Walk-Through, and will review the anticipated HIPAA Security Final Rules. “This Program has been approved for 1.5 HR (General) Recertification Credit Hours toward aPHR®, aPHRi®, PHR®, PHRca®, SPHR®, GPHR®, PHRi®, and SPHRi® recertification through HRCI.”
Speaker Biographies can be found on our website on the event page for this program.
Speaker Bios
Dorothy Cociu
Dorothy Cociu RHU, REBC, GBA, RPA, is the President of Advanced Benefit Consulting and has 35+ years of experience in the operations, sales and administration of employee benefit programs and compliance related to health plan administration, ERISA, COBRA, HIPAA and other laws, such as ACA, FFCRA, CARES Act, and Transparency in Coverage Rules (2020), Consolidated Appropriations Act of 2021 (CAA), and One Big Beautiful Act. Dorothy began her administrative experience began in the Taft-Hartley marketplace, then moved to self-funded administration after three years. She spent nearly a decade in the TPA business, primarily for Taft Hartley then self-funded administration. She began as an auditor, where she was trained on all audit procedures, which are consistent with current government audits. She then moved to a health insurance General Agency, and later, developed Advanced Benefit Consulting, where she is the President and primary consultant for plan sponsor clients on employee benefits and benefit compliance.
Carl Grifka
Carl is a Principal at Newport Consulting LLC and Alpha Secure LLP, and is a dynamic finance and IT thought leader with experience within public accounting, a global cinema technology leader, and a global Fortune 100 company. Carl leverages his deep IT and business process background in his role as a technology and process risk adviser to CFO’s, CIO’s, CISOs and CEO’s of SEC filers and private businesses. Carl maintains his CISSP, CISA, CISM, PMP, CDPSE, and lean six sigma green belt certifications.
Carl and his team guide clients through complex systems initiatives leveraging their vast business and technology experience to govern, deploy, and manage these initiatives. Carl also advises members of management, boards and executives regarding SOX (business and IT), IT planning and IT assurance, cybersecurity, SOC, and organizational change management. Carl serves on the Board of ISACA LA and maintains a solid understanding of new and emerging topics impacting the profession.