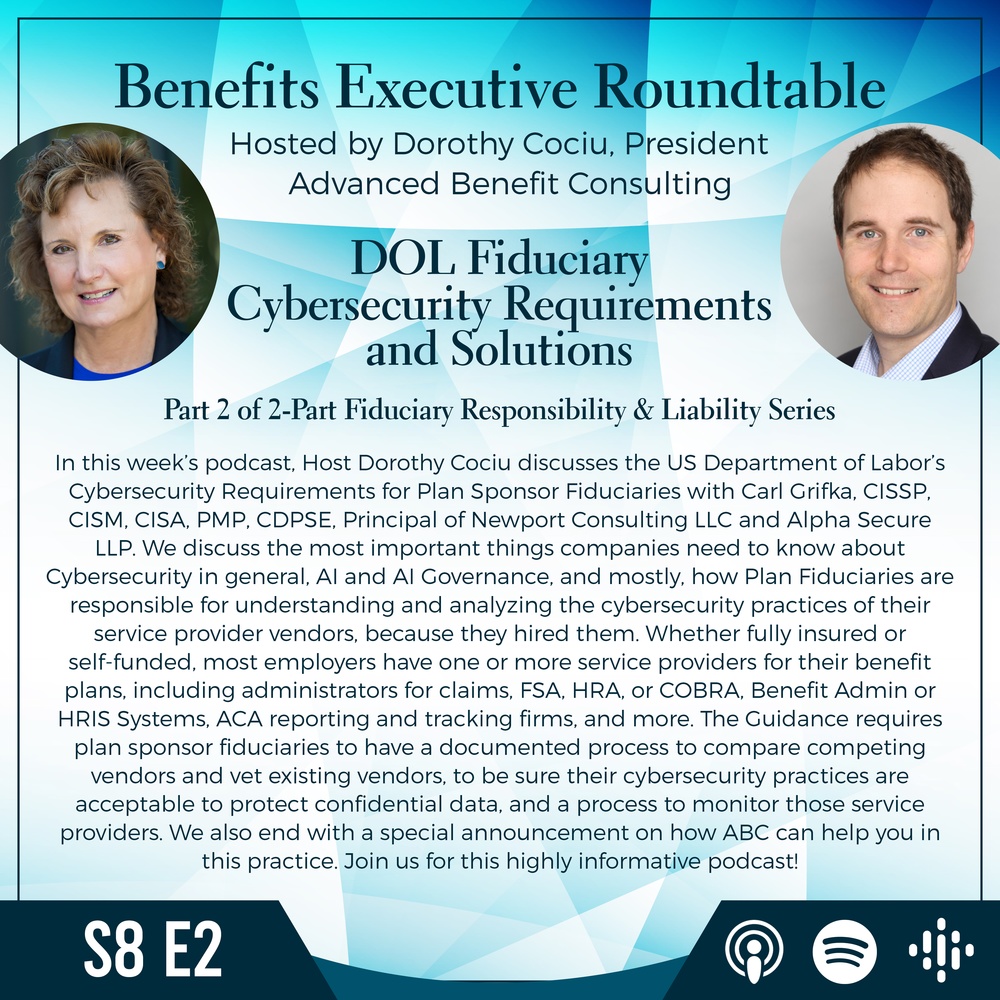
Part 2 of 2-Part Fiduciary Responsibility & Liability Series
In this week’s podcast, Host Dorothy Cociu discusses the US Department of Labor’s Cybersecurity Requirements for Plan Sponsor Fiduciaries with Carl Grifka, CISSP, CISM, CISA, PMP, CDPSE, LSSGB, Principal of Newport Consulting LLC and Alpha Secure LLP. We discuss the most important things companies need to know about Cybersecurity in general, AI and AI Governance, and mostly, how Plan Fiduciaries are responsible for understanding and analyzing the cybersecurity practices of their service provider vendors, because they hired them. Whether fully insured or self-funded, most employers have one or more service providers for their benefit plans, including administrators for claims, FSA, HRA, or COBRA, Benefit Admin or HRIS Systems, ACA reporting and tracking firms, and more. The Guidance requires plan sponsor fiduciaries to have a documented process to compare competing vendors and vet existing vendors, to be sure their cybersecurity practices are acceptable to protect confidential data, and a process to monitor those service providers. We also end with a special announcement on how ABC can help you in this practice. Join us for this highly informative podcast!
Show Notes